October 30, 2026
What the French Supermarket Cyberattack Means for Food Retailers, Manufacturers and Food Safety
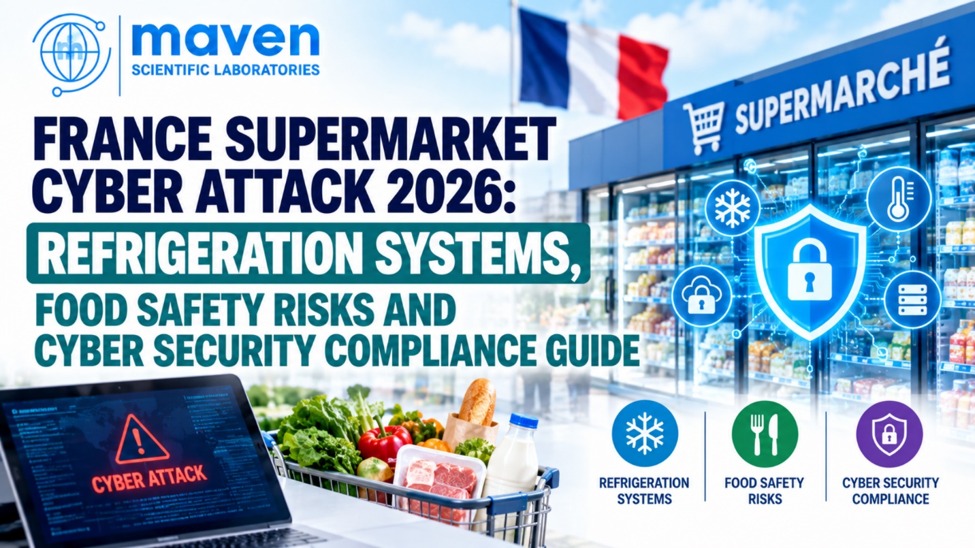
On 12 October 2026, a large-scale cyberattack disrupted refrigeration systems across hundreds of supermarkets in France, forcing retailers to discard significant quantities of fresh and frozen food.
Attackers reportedly manipulated connected refrigeration-control systems, causing temperatures in some cold rooms and refrigeration units to rise to approximately 50°C (122°F). The incident resulted in widespread food spoilage, operational disruption and reports of fires at some affected locations. French authorities opened an investigation, with the country's cybersecurity agency ANSSI involved in the response.
The incident affected multiple major retail networks, including Intermarket, Netto, Cooperative U, Carrefour, E.Leclerc and Monoprix, according to reporting from French media.
The incident is particularly significant because the attack did not primarily target customer databases or payment systems. Instead, attackers manipulated operational technology (OT) and connected refrigeration infrastructure that directly supports food preservation and cold-chain integrity.
This demonstrates that cybersecurity can increasingly become a food safety and product-quality issue, particularly where Internet-connected equipment controls temperature-sensitive products.
Why the Supermarket Refrigeration Cyberattack Matters
Modern supermarkets increasingly rely on connected systems to monitor and control:
- Refrigerators and freezers
- Cold rooms
- Frozen-food storage
- Temperature monitoring
- Defrost cycles
- Refrigeration compressors
- Energy-management systems
- Remote equipment monitoring
- Automated alarms
These technologies can improve energy efficiency, maintenance and operational visibility. However, connectivity can also introduce cybersecurity vulnerabilities.
In the October 2026 incident, attackers reportedly manipulated refrigeration settings and caused defrost operations to run for substantially longer than normal. In at least some locations, temperatures reached around 50°C, resulting in extensive product losses.
Key Cybersecurity-to-Food-Safety Risk
|
Cybersecurity Weakness |
Operational Consequence |
Food Safety Impact |
|
Exposed connected controllers |
Unauthorized system access |
Loss of temperature control |
|
Outdated firmware |
Exploitation risk |
Product spoilage |
|
Weak remote access controls |
Unauthorized configuration changes |
Cold-chain disruption |
|
Delayed alarms |
Slower incident response |
Extended temperature excursions |
|
Unsupported equipment |
Limited security updates |
Increased cyber risk |
|
Poor network segmentation |
Attack propagation |
Wider operational disruption |
The incident therefore highlights a broader principle:
A cybersecurity failure in food infrastructure can become a physical product-safety event.
What Happened in France?
The attack occurred overnight between 11 and 12 October 2026 and affected refrigeration systems used by multiple French retailers.
Reports indicate that attackers remotely manipulated refrigeration settings, including forced defrost operations. In some locations, cold storage temperatures reached approximately 50°C.
The attack reportedly affected around 300 Intermarket and Netto stores, alongside numerous Cooperative U stores and other retailers. Reuters reported that Intermarket had approximately 150 affected stores, while other reporting identified additional affected retail locations. The precise overall number has varied as retailers continued assessing the incident.
Some retailers reportedly experienced fires in addition to food losses.
French authorities, including ANSSI, began investigating the incident. France also coordinated with European counterparts because similar security issues were reported or investigated in other European markets.
How Were Refrigeration Systems Affected?
The affected systems were connected refrigeration-management technologies used to monitor and control commercial refrigeration.
Danfoss confirmed that it was aware of incidents in France involving a limited number of refrigeration-management systems and stated that affected units were running outdated firmware.
French reporting also identified vulnerabilities and compromises involving refrigeration-control technologies from other suppliers, including Dixwell and Copeland, indicating that the cybersecurity issue may extend beyond a single equipment manufacturer.
Importantly, the exact attack pathway and responsible threat actor remain under investigation.
Refrigeration Cyberattack Risk Chain
- Internet-connected equipment
↓
- Vulnerable / outdated control technology
↓
- Unauthorized access
↓
- Remote manipulation of refrigeration settings
↓
- Temperature excursion
↓
- Food spoilage
↓
- Food waste + financial losses + potential safety incidents
↓
- Business continuity and food-supply disruption
Which Food Retailers and Systems Should Pay Attention?
The incident is relevant to organizations operating temperature-controlled environments, not only supermarkets.
|
Business / Sector |
Key Cybersecurity Consideration |
Potential Food Safety Impact |
|
Supermarkets |
Refrigeration network security |
Food spoilage |
|
Hypermarkets |
OT and IT segmentation |
Large-scale cold-chain disruption |
|
Food warehouses |
Remote refrigeration access |
Inventory losses |
|
Cold-storage operators |
Controller security |
Temperature excursions |
|
Food manufacturers |
Production refrigeration |
Product-quality risks |
|
Pharmaceutical retailers |
Temperature-controlled storage |
Product integrity risks |
|
Food distributors |
Cold-chain monitoring |
Distribution disruption |
|
Restaurant chains |
Connected refrigeration |
Perishable-food losses |
|
Equipment manufacturers |
Secure-by-design controls |
Product cybersecurity |
|
Refrigeration service providers |
Remote administration |
Third-party access risks |
Companies should therefore consider refrigeration infrastructure as part of their critical operational technology environment, rather than treating it solely as an engineering or facilities-management issue.
Cybersecurity Is Becoming a Food Safety Issue
Traditionally, food safety programs have focused on:
- Microbiological Hazards
- Chemical contamination
- Physical contamination
- Temperature control
- Sanitation
- HACCP systems
- Traceability
- Supplier controls
The French incident demonstrates why organizations should also consider cybersecurity-related operational failures within their food-safety and business-continuity frameworks.
A malicious change to a refrigeration controller can produce the same practical consequence as a mechanical refrigeration failure: unsafe or unsuitable storage conditions.
The difference is that a cyberattack can potentially manipulate multiple connected systems simultaneously.
Cold-Chain Integrity and Temperature Excursions
Cold-chain management is particularly sensitive because many food products require controlled storage temperatures throughout their lifecycle.
A cyber-induced temperature excursion may affect:
- Meat and poultry
- Seafood
- Dairy products
- Frozen foods
- Prepared foods
- Fresh produce
- Chilled beverages
- Temperature-sensitive ingredients
Once refrigeration fails, retailers may need to determine:
- When the temperature deviation started.
- How long the products were exposed.
- Which products were affected.
- Whether food-safety limits were exceeded.
- Whether products can be released or must be destroyed.
- Whether regulators or insurers must be notified.
- Whether affected inventory can be traced.
This makes temperature monitoring, alarm integrity and incident records important components of both cybersecurity and food-safety management.
What Manufacturers of Refrigeration Equipment Should Consider
The incident also has implications for manufacturers and suppliers of connected refrigeration technologies.
Equipment manufacturers should consider:
1. Secure-by-Design Engineering
Cybersecurity should be integrated into refrigeration equipment from the design stage rather than treated as an after-sales issue.
2. Firmware Lifecycle Management
Manufacturers should clearly define:
- Supported firmware versions
- Security update periods
- End-of-support dates
- Vulnerability notification processes
- Upgrade procedures
3. Secure Remote Management
Remote monitoring and configuration capabilities should incorporate appropriate authentication, authorization and encryption controls.
4. Vulnerability Disclosure
Manufacturers should maintain processes for:
- Vulnerability identification
- Customer notification
- Security advisories
- Patch distribution
- Remediation guidance
5. Legacy Equipment Management
Organizations operating older refrigeration controllers should receive clear guidance regarding:
- End-of-life status
- Security limitations
- Replacement options
- Migration procedures
Third-Party and Supplier Cybersecurity Risk
The incident also demonstrates the importance of managing cybersecurity risks introduced by third-party technology providers.
Supermarket operators may not manufacture or directly manage their refrigeration controllers. Instead, they may depend on:
- Refrigeration manufacturers
- Maintenance contractors
- IT service providers
- Cloud platforms
- Remote-monitoring providers
- System integrators
- Equipment distributors
This creates a supply-chain cybersecurity challenge.
Companies should therefore include cybersecurity requirements in supplier qualification and contract management.
Supplier Cybersecurity Review
|
Supplier Area |
Questions to Assess |
|
Equipment |
What controllers and software are installed? |
|
Firmware |
Are systems currently supported? |
|
Security |
What vulnerabilities have been identified? |
|
Remote Access |
Who can access the equipment remotely? |
|
Authentication |
How are privileged accounts protected? |
|
Updates |
How are security patches delivered? |
|
Monitoring |
Are abnormal changes detected? |
|
Incident Response |
How quickly will the supplier notify customers? |
|
Lifecycle |
When does the equipment reach end of support? |
|
Documentation |
Are security advisories and technical records available? |
Frequently Asked Questions
1. What happened in the France supermarket cyberattack?
Attackers compromised or manipulated connected refrigeration systems at numerous French supermarkets, causing refrigeration units and cold-storage systems to heat up dramatically and resulting in widespread food losses.
2. How hot did some refrigerators become?
Reports indicated that some affected refrigeration and cold-storage systems reached approximately 50°C (122°F).
3. Which retailers were affected?
Reportedly affected retailers included Intermarket, Netto, Cooperative U, Carrefour, E.Leclerc and Monoprix, although the precise scope continued to evolve as investigations progressed.
4. Was Danfoss equipment involved?
Yes. French authorities and reporting identified vulnerabilities involving refrigeration-control technology supplied by Danfoss. Danfoss said affected systems were running outdated firmware.
5. Was the attack caused by a Danfoss vulnerability?
The affected refrigeration-control technology has been identified, but the exact exploitation route and responsible attackers remain subject to investigation. Organizations should avoid treating the precise technical root cause as finally established.
6. Is this a food safety issue?
Yes. A cyberattack that disrupts refrigeration can directly affect temperature control, food preservation and product disposition. The event demonstrates the need to integrate cybersecurity with food-safety and cold-chain risk management.
7. Does cybersecurity apply to food retailers?
Absolutely. Connected refrigeration, warehouse-management systems, IoT devices and other operational technologies can become attack surfaces capable of producing physical consequences.
8. What should retailers do first?
Retailers should identify Internet-connected refrigeration equipment, review firmware and support status, secure remote access, segment OT networks and verify independent temperature monitoring.
9. Should suppliers be reviewed?
Yes. Third-party refrigeration and maintenance providers can have privileged access to critical operational systems and should be included in cybersecurity risk assessments.
10. Can cybersecurity failures cause physical product losses?
Yes. The French incident demonstrates that manipulation of connected operational equipment can cause physical disruption, food spoilage and potentially equipment damage.
Conclusion
The October 2026 French supermarket cyberattack is an important warning for the food industry: cybersecurity and food safety are increasingly interconnected.
The incident reportedly caused refrigeration systems to reach temperatures of up to 50°C, resulting in significant food spoilage and operational disruption across numerous supermarkets. Investigations have identified refrigeration-control technology, including Danfoss systems, while the precise attack mechanism and responsible actors remain under investigation.
For food retailers, manufacturers, cold-storage operators and technology suppliers, cybersecurity should no longer be treated solely as an IT responsibility.
A resilient food-safety strategy should address the complete chain:
Connected equipment → Cybersecurity → Temperature control → Cold-chain integrity → Food safety → Business continuity
Organizations should therefore assess connected refrigeration infrastructure, eliminate unnecessary Internet exposure, maintain supported firmware, strengthen remote access, segment operational networks and establish independent temperature-monitoring and emergency-response procedures.
The key lesson is simple:
A cyberattack on food infrastructure can become a food safety incident in minutes.
How Maven Regulatory Solutions Can Help
Maven Regulatory Solutions can support companies with:
- Food industry regulatory compliance assessments
- Food safety and cybersecurity risk assessments
- Cold-chain compliance reviews
- Supplier compliance assessments
- Product safety and quality risk assessments
- Regulatory gap assessments
- Risk-management documentation
- Supply-chain compliance assessments
- Third-party vendor assessments
- Regulatory intelligence
- Compliance monitoring
- Business continuity and operational risk support
- Food and consumer-product regulatory consulting
Our approach helps organizations identify vulnerabilities at the intersection of cybersecurity, food safety, product quality and regulatory compliance, supporting stronger and more resilient supply chains.
Post a comment